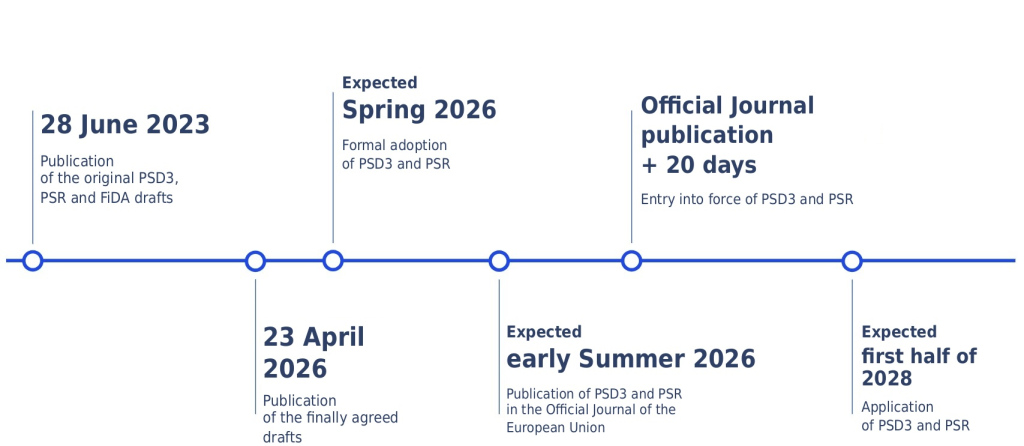
On April 23, 2026, the EU Parliament, Council and European Commission agreed on final versions of PSD3 (Payment Services Directive 3) and the PSR (Payment Services Regulation). This paves the way for a fundamental reform of European payments law.
For credit institutions, e-money institutions and payment service providers (PSPs), this means that they should review their compliance structures, contractual regulations and IT architecture at an early stage and adapt them where necessary.
The accompanying Open Finance Initiative (Financial Data Access, FIDA), which was initially launched in parallel, was largely “on hold”; however, following the recent resumption of compromise efforts in the Council, progress in negotiations can also be expected in this area in the near future.
An overview of the key changes according to the final drafts
Existing licenses: (Re-)authorization and grandfathering for existing institutions
Existing payment institutions and e-Money institutions must actively review their license and have them reconfirmed. In principle, there is an obligation to submit a (re)confirmation within the transitional periods provided for.
However, automatic authorizations and register entries will be made as a rule. This requires evidence to be submitted to the supervisory authority that the institution also meets the stricter requirements (e.g. with regard to resolution plans, including ensuring outsourcing continuity).
Fraud prevention
The requirements for fraud prevention will be significantly expanded. Payment service providers must further develop their monitoring systems and explicitly use new technologies such as artificial intelligence, provided this is suitable for risk detection. At the same time, liability risks are increasing: Deficits in monitoring may lead to greater claims for reimbursement in future.
The exchange of data to combat fraud is made easier, but remains subject to strict data protection requirements, such as purpose limitation or data protection impact assessments.
Obligations to cooperate are also new: Providers of electronic communication services and very large online platforms or search engines must be more involved in fraud prevention.
A central instrument is the Verification of Payee. The content of this is being significantly sharpened:
Extension to all credit transfers, even outside SEPA,
Narrowly limited opt-out options in the B2B area,
clearly regulated liability and recourse relationships between the payment service providers involved.
Strong customer authentication
The specifications for strong customer authentication (SCA) will be further developed and harmonized.
What is new in this respect is a clear perspective of inclusion: payment service providers must offer suitable authentication solutions free of charge to user groups with special needs – for example, without a smartphone.
Another component is the mandatory authorization dashboard. Payment service providers must provide a central overview in their customer interface where users can manage the access they have granted to third-party providers – including transparency regarding the purpose, scope and duration of consent as well as clearly regulated revocation and logging functions.
The regulations also introduce new obligations and liability rules for technical service providers, particularly in the context of outsourcing. Liability risks are generally limited to direct damage. It remains unclear whether this will also apply in the case of European Digital Identity Wallets that are to be recognized as mandatory in the future and offered by the member states qualify as SCA under eIDAS.
Open Finance
Access to payment accounts and payment systems will be regulated more precisely. In future, account-holding institutions may only refuse or withdraw access for third-party providers under narrowly defined conditions, for example in the event of demonstrably “serious” risks – particularly in connection with money laundering prevention.
The aim is to create a level playing field between banks and non-bank payment service providers.
Originally, this regime was to be supplemented by the proposal for a Financial Data Access Framework (FiDA). As things stand, movement is expected in the trilogue negotiations from summer 2026.
Protection of customer funds
The requirements for safeguarding customer funds will be standardized and at the same time tightened. Particularly for E-money institutions, in future, a much stricter deadline for securing incoming funds will apply for the T+1 logic.
There are also new specific requirements for managing concentration risks, for example for custodians or hedging instruments. In addition, payment service providers will have to report significant changes to their hedging measures in advance.
The new framework also clarifies the handling of funds in connection with e-money token sand dovetails the requirements with the Markets in Crypto-Assets Regulation (MiCA).
Alignment with the MiCA framework
In order to avoid double regulation, the package contains specific delimitations to the MiCA Regulation. Payment service providers with PSD3 -MiCA license holders can provide certain crypto-related services in connection with e-money tokens without additionally requiring a separate MiCA license.
However, they must fulfill the corresponding notification and information obligations and comply with certain lead times.
Exemption regime
The existing exceptions will be revised and clarified.
One focus is on the Europe-wide harmonization of the commercial agent exemption, which has so far been interpreted differently.
The legislator also clarifies the conditions under which the “limited network” exemption applies. The aim is to reduce regulatory gray areas and sharpen the distinction between regulated and unregulated business models.
Background to the reform of payment law
PSD3 and PSR are intended to harmonize regulation
By transferring central behavior-related regulations to the PSR, the legislator is pursuing the goal of reducing national implementation leeway and thus regulatory fragmentation. This increases legal and planning certainty, but also leads to more uniform and stricter enforcement of the regulations with less room for national interpretation.
More security and fraud prevention
The new features place even greater emphasis on security and fraud prevention. Strong Customer Authentication (SCA), improved transaction monitoring and (re)introduction of the IBAN name matching are intended to reduce risks and strengthen trust in digital payments. The tightening of liability and reimbursement in cases of fraud is also operationally challenging: Similar to the UK and Singapore, PSPs will have to reimburse losses incurred by bank customers in certain constellations of fraud. At the same time, it will become easier – and in some cases mandatory – to exchange fraud data. There will be limited possibilities for recourse against telecommunications companies whose infrastructure has been used by fraudsters.
The regulatory framework for open banking is also being further developed. Dedicated, secure interfaces and clear rules on interface governance are intended to increase availability and quality; customers are to be given more transparency and control over data access, for example via authorization dashboards.
Strengthening consumer protection and transparency
The information obligations towards customers will be specified, in particular with regard to currency conversion fees and the blocking of funds. As a result, many institutions will have to revise the content and editing of their general terms and conditions, customer information and product-related documents.
How companies should prepare for PSD3 and the PSR
Credit institutions, payment institutions, e-money institutions and AIS/PIS providers should (have) an integrated legal and operational gap analysis carried out at an early stage so that the requirements of PSD3/PSR are translated into processes, controls, IT and contracts in a verifiable manner.
The most efficient approach is one in which legal departments and second-line managers work closely together and translate the regulatory interpretation directly into an actionable operating model – especially for GRC, third-party/outsourcing governance, contracting, SCA/fraud controls and API/interface governance.
We regularly work in close cooperation with the implementation experts at KPMG AG Wirtschaftsprüfungsgesellschaft, who deal with corresponding implementation issues here, among other things.
Before employees are granted access to sensitive information or perform security-sensitive tasks as part of an assignment, their reliability must be verified through a special…
After being postponed twice, the EU Deforestation Regulation (EUDR) is expected to take effect on December 30, 2026. Companies that handle certain products derived…
AI can assist executive boards, supervisory boards, and managing directors in making decisions. However, unverified results can create liability risks. Fraport General Counsel Thomas Stoll…
In light of geopolitical changes, new trade barriers, and more rigorous audits, customs and foreign trade law are increasingly becoming a focus for companies. The…
With the implementation of the new EU Environmental Criminal Law Directive, the environment is becoming a core area of managerial liability. Managers face reputational damage,…
Two critical vulnerabilities in the PHP programming language are threatening web applications and digital products worldwide. The Federal Office for Information Security (BSI) has warned…
The rapid advancement of artificial intelligence presents corporate leadership with diverse and far-reaching decisions. These decisions concern not only the selection and deployment of appropriate…
The current issue of PERSONALFÜHRUNG (10–11/2026) features two articles by female experts from KPMG and KPMG Law.
In the article “Will AI Save the Day?…
KPMG International does not provide services to clients. No member firm is authorised to bind or contract KPMG International or any other member firm to any third party, just as KPMG International is not authorised to bind or contract any other member firm.