The EU’s NIS 2 Directive is intended to ensure greater cyber security for essential infrastructures and create a uniform and significantly higher level of protection in Europe. The member states were supposed to transpose it into national law by October 17, 2024. The German legislator has not yet fulfilled this obligation. However, a draft of the implementation law (NIS2UmsuCG) has been available since July 2024. The next government will also have to ensure that the directive is implemented. The directive prescribes certain risk management measures such as tests for major infrastructure companies and tightens reporting obligations.
NIS-2 expands the scope of obligated companies enormously
Cybersecurity measures were already mandatory in the past. However, the NIS 2 Directive significantly expands the group of companies affected. The critical sectors compared to the NIS Directive adopted in 2016 have been expanded by eleven sectors. In addition to operators of essential services, providers of digital services that were not previously covered by the regulations are now also affected. These include, for example, providers of cloud services, data centers and online marketplaces. Ultimately, almost any large company may fall within the scope of application in future. In addition, it is not always clear at first glance whether a company is affected. Particularly in group structures, the parent company may also be obliged due to shareholdings.
Companies must determine their own impact
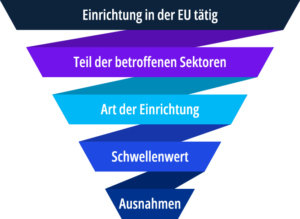
The NIS-2 Directive and the NISUmsuCG are aimed at operators of critical infrastructure, particularly important facilities and important facilities. In the last two categories, the sector and criteria such as annual turnover and annual balance sheet total determine who is affected. Whether an institution is affected by NIS 2 or the NISUmsuCG must be determined by the institution itself. The Federal Office for Security and Information Technology (BSI) offers a NIS 2 impact assessment for initial orientation. In principle, companies can assess whether they are affected by NIS 2 in five steps:
How companies can increase their cyber security
A number of laws are to be amended in Germany to implement the directive. Most of the changes concern the Act on the Federal Office for Information Security (BSI Act – BSIG). In particular, stricter cyber security requirements are planned. Companies will have to take not only technical but also organizational measures to ensure the protection of their IT infrastructure. In particular, these additional obligations will be imposed on the companies concerned:
The Implementation Act defines a number of risk management measures. These include concepts for risk analyses, backups, tests, encryption and training.
Particularly important facilities and important facilities must report security incidents to a reporting office.
The companies concerned must register as such independently.
In the event of security incidents, affected companies must inform other organizations affected by the incident.
Members of the Executive Board are personally obliged to monitor the implementation of risk management measures.
Additional verification obligations apply to operators of critical infrastructures.
The management is personally liable
If affected facilities do not meet the requirements, they could face fines of up to 10 million euros or 2 percent of their global annual turnover. The personal liability of the management is particularly controversial. The liability standard of the current draft of the German Implementation Act corresponds to the requirements of the NIS-2 Directive. Management boards are already liable if they violate their duties to ensure IT security without due care and this results in damage. NIS 2 significantly increases the de facto liability risk for management boards: management bodies must approve the risk management measures taken in the area of cyber security and monitor their implementation. They can be held liable for violations. The current government draft of the NIS2UmsuCG may even increase the responsibility of management boards in terms of wording by requiring them to implement the risk management measures in addition to monitoring them.
How companies should prepare
Affected companies should deal with NIS 2 even before an implementation law comes into force and take appropriate and proportionate measures based on comprehensible risk management. All measures should be based on a holistic and threat-oriented management approach that aims to prevent security incidents or minimize their impact. We recommend the following steps:
- First of all, all companies should carry out an impact analysis.
- If it is affected, the next step is a readiness assessment. Companies should check how the company is positioned in terms of IT security and what measures are still necessary in relation to NIS 2.
- From this analysis, it then derives the measures that are still necessary and implements them.
- Companies should set up NIS 2 governance to ensure that all measures are in place.
- Companies should train their management and employees, particularly in the areas of law, data protection, audit / revision, cyber security and technology.
- Finally, a process should be set up for mandatory reporting to the supervisory authority.
- The entire implementation should be subject to regular monitoring.